Guides / October 22, 2026
Active Exploitation of a Network Management Plane Starts the 72 Hour Clock
Defense Federal Acquisition Regulation Supplement (DFARS) clause 252.204-7012 sets a hard reporting duty. Contractors must rapidly report cyber incidents within 72 hours. Active exploitation of your network management plane tests that duty.
A software-defined wide area network (SD-WAN) links branch sites over shared connections. VeloCloud Orchestrator (VCO) is the web console that manages it. Arista confirms active exploitation of a flaw in on-premises VCO. The flaw is tracked in the Common Vulnerabilities and Exposures program as CVE-2026-114625.
Why this flaw matters for reporting
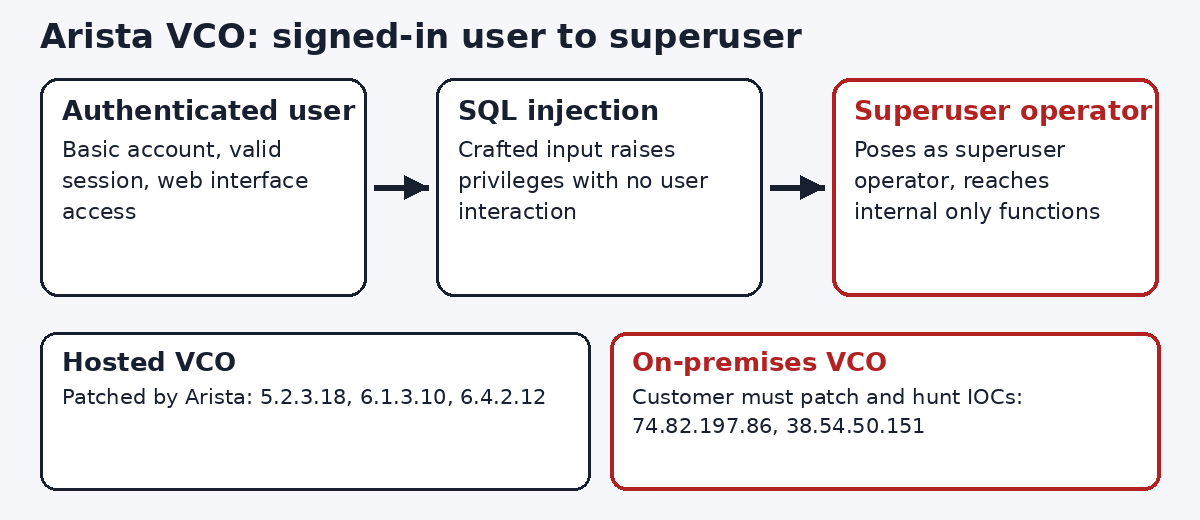
The attack needs a valid signed-in session. A Structured Query Language (SQL) injection path raises privileges. Any authenticated user can gain operator rights. That user can pose as a local superuser operator.
The console manages edge devices and network data. Compromise may harm confidentiality, integrity, and availability. If that console serves covered networks, treat signs seriously.
The clock question to answer first
The clock turns on discovery of an incident. A vendor headline alone is not your incident. Evidence of compromise on your system is different.
Hunt first, and hunt fast. Arista published indicators of compromise (IOCs) for this flaw. The two Internet Protocol (IP) addresses are 74.82.197.86 and 38.54.50.151. Check connections, logs, and administrator activity against both.
Arista also flags odd paths and encoded characters. It flags references to internal services. Preserve web, backend, system, and database logs now. Preservation supports any report you must file.
Patch state is part of the record
Arista patched its hosted service already. The patched levels are 5.2.3.18, 6.1.3.10, and 6.4.2.12. On-premises customers must patch their own systems. Record your version before and after patching.
PolicyCortex does not patch Arista gear. Name the owner who does in your incident file.
The governance lesson
Management planes are part of the system. Inventory every orchestrator and its covered data links. Governance means you fully understand what an incident there touches.
What to do this week
Run the IOC hunt on every on-premises orchestrator. Preserve the logs before you patch. Decide the reporting question from evidence, not headlines.
Sources
- Arista Security Advisory 0199, October 22, 2026.
- CVE-2026-114625 record, CVE Program. The record is in reserved state at publication time.
- BleepingComputer, Arista patches new VeloCloud Orchestrator zero-day. https://www.bleepingcomputer.com/news/security/arista-patches-new-velocloud-orchestrator-zero-day-exploited-in-attacks/
- DFARS clause 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting.
- Original diagram by PolicyCortex.
Next step
Want incident evidence gathered before the clock runs out? See how PolicyCortex collects it from the live system.