Guides / October 23, 2026
Atlassian Flaw and the 72-Hour Rule When Credentials May Be Read
CVE is Common Vulnerabilities and Exposures. CVE-2026-21589 lets an unauthenticated attacker read server files. The attacker only needs the exact file name and path.
Atlassian warns that some configurations expose sensitive files. Credentials are named outright. A flaw that can read credentials is not a routine bug.
When this becomes a reportable incident
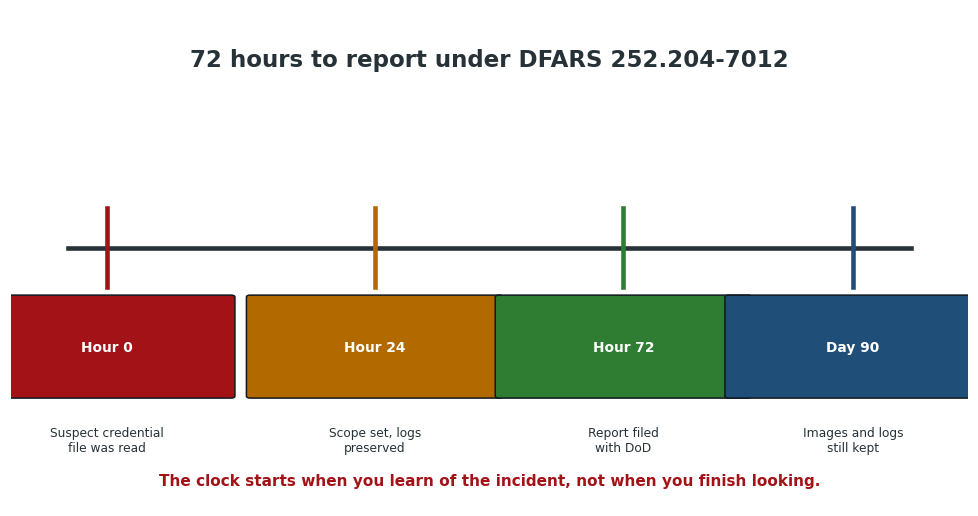
DFARS is the Defense Federal Acquisition Regulation Supplement. Clause 252.204-7012 requires a cyber incident report to DoD within 72 hours.
The trigger is discovery of a cyber incident. If logs or forensics show that a credential file may have been read, the clock starts.
Eight products share the vulnerable component. Bitbucket Data Center, Confluence Data Center, Jira Software Data Center, and Jira Service Management Data Center are in range. Bamboo Data Center, Crowd Data Center, Crucible, and Fisheye are in range too.
CISA added the flaw to its Known Exploited Vulnerabilities catalog on October 15, 2026. CISA is the Cybersecurity and Infrastructure Security Agency. Active exploitation makes the incident question real, not theoretical.
What to preserve
Keep images and logs for 90 days. Preserve the web server logs from the affected products. Preserve authentication logs and any disk images you take.
Record what you looked for and what you found. If you rule out compromise, keep that record too. It is your proof that the 72-hour clock never started.
What to do this week
Patch to the fixed builds. Check access logs for requests that name sensitive paths. If anything suggests a credential file was read, start the incident process and the 72-hour count.
Sources
- Atlassian security advisory for CVE-2026-21589, Atlassian, October 5, 2026. https://confluence.atlassian.com/security/cve-2026-21589-arbitrary-file-access-vulnerability-impacts-multiple-products-1870495748.html
- CVE-2026-21589 record, CVE Program.
- Emergency Threat Response: CVE-2026-21589, Rapid7. https://www.rapid7.com/blog/post/etr-cve-2026-21589-critical-unauthenticated-arbitrary-file-access-in-atlassian-products/
- CERT-EU Security Advisory 2026-015, CERT-EU. https://cert.europa.eu/publications/security-advisories/2026-015
- Original diagram by PolicyCortex.
More incident reporting guides live at dfarsreadiness.com.
Pull the last 30 days of web logs for your self hosted Atlassian servers before you patch.