Guides / October 26, 2026
BeyondTrust KEV Flaw Is a DFARS 7012 Incident Readiness Test
Incident readiness is proven by the record you already hold. A KEV flaw in a privileged tool is the test.
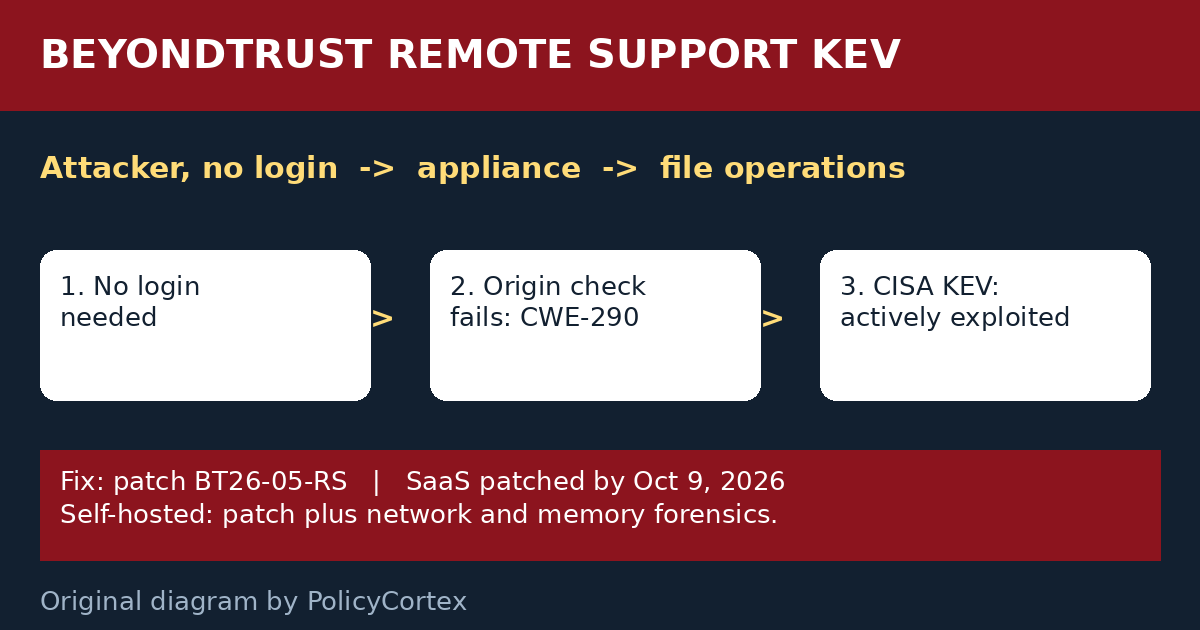
On October 15, 2026, BeyondTrust published security advisory BT26-05. It fixes a flaw in Remote Support scoring 9.3 under Common Vulnerability Scoring System (CVSS) version 4.0. A remote attacker with no login can perform file operations on the appliance. The weakness is Common Weakness Enumeration (CWE) 290, improper origin validation.
The flaw and the KEV listing
Common Vulnerabilities and Exposures (CVE) is the public record system.
- CVE-2026-102764: improper origin validation flaw in an internal messaging component. A remote attacker with no login can perform file operations on the appliance.
All Remote Support versions 26.2.3 and earlier are affected. The Cybersecurity and Infrastructure Security Agency (CISA) added it to its Known Exploited Vulnerabilities (KEV) catalog. That listing came on October 16, 2026. The due date was October 19, 2026. CISA says threat actors are actively exploiting the flaw. They use it to gain initial access, then establish persistence, escalate privileges, and move laterally.
What readiness looks like here
Safeguarding a privileged tool means more than patching it. Patch BT26-05-RS covers self-hosted versions 24.3.1 and later. Versions older than 24.3.1 must upgrade first. BeyondTrust patched SaaS customers by October 9, 2026.
Then comes the part teams skip. CISA urges network and memory forensics on self-hosted appliances. Run them. Keep the dated result with the patch record. That pair is what incident review needs: what was fixed, and whether anyone got in first.
A team that can show both answers fast is ready. A team with only a patch ticket is still guessing.
Sources
- BeyondTrust security advisory BT26-05, BT26-05, October 15, 2026.
- CISA alert, CISA Urges Patching Critical Vulnerability in BeyondTrust Remote Support, October 16, 2026.
- CISA Known Exploited Vulnerabilities catalog, Known Exploited Vulnerabilities Catalog, listing dated October 16, 2026.
- CVE-2026-102764 record, CVE Program.
- Original diagram by PolicyCortex.
Next step
Want safeguarding evidence linked without chasing spreadsheets? See how PolicyCortex collects it from live systems.