Guides / October 23, 2026
A Root-Level Appliance Flaw Can Start the DFARS 7012 Clock
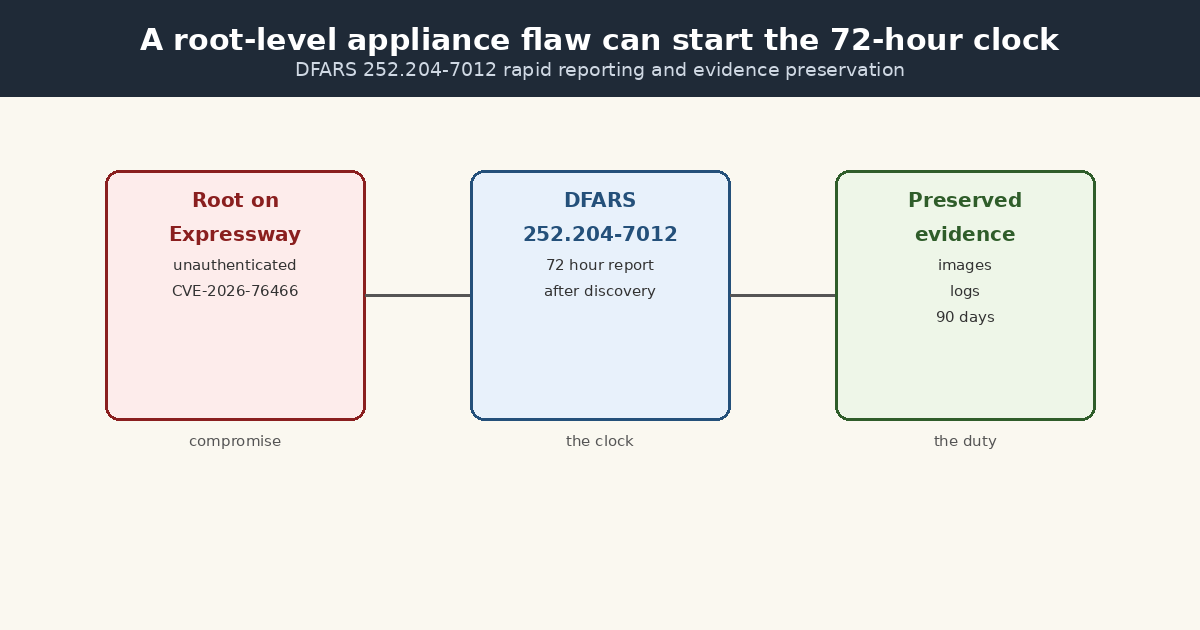
Defense Federal Acquisition Regulation Supplement (DFARS) clause 252.204-7012 is about incidents. A new Cisco flaw shows how fast an appliance can become one.
Cisco published hardening releases on October 21, 2026. The worst flaw gives an unauthenticated remote attacker root on clustered Expressway.
The flaw that could become an incident
The record is CVE-2026-76466. Common Vulnerabilities and Exposures (CVE) is the record system.
The flaw is in the database service of clustered Expressway-C and Expressway-E. An attacker with network access can run OS (operating system) commands as root. No login is needed. Cisco scores it 9.8.
Expressway-E often sits in the DMZ (demilitarized zone). It is reachable from the internet by design. Root there is a foothold an attacker can use to pivot inward.
The fix is X15.5.20. Cisco lists no workaround. Cisco knows of no malicious use as of October 21, 2026.
When the 72 hour clock starts
Clause 7012 requires a rapid incident report. The report is due within 72 hours of discovery. Discovery means you discover a cyber incident.
A new CVE alone is not an incident. Evidence of use on your appliance is different. Log review and forensics decide that question.
Do not wait for perfect proof before reporting. The clause expects a report while facts develop. Your team can update the report later.
The 90 day evidence duty
Clause 7012 also requires evidence preservation. You must preserve images and relevant files. The preservation period is 90 days minimum.
That duty covers the affected appliance itself. It also covers logs and monitoring records. Preserve before any rebuild or reset work.
For this flaw, keep Expressway logs from before the patch date. Keep the patch ticket with before and after versions. Keep the scan that confirmed the fix.
PolicyCortex does not patch Cisco products. Vendors ship those fixes. PolicyCortex helps teams keep incident evidence organized.
What to do this week
Check whether you run clustered Expressway on an affected release. Review appliance logs for unusual database service connections. Preserve relevant records before patching.
Sources
- CVE-2026-76466 record, CVE Program.
- Cisco Security Advisory cisco-sa-vcs-static-cred-hr7EWZ8t, Cisco Expressway Series Remote Code Execution Vulnerability, October 21, 2026. https://sec.cloudapps.cisco.com/security/center/content/CiscoSecurityAdvisory/cisco-sa-vcs-static-cred-hr7EWZ8t
- DFARS clause 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting.
- Original diagram by PolicyCortex.
Next step
Want incident evidence kept in one dated record? See how PolicyCortex organizes it from live systems.