Guides / October 24, 2026
Web Shells on a Nextcloud Server Start the DFARS Incident Clock
A patched server can still be a compromised server. That is the line that matters for defense contractors.
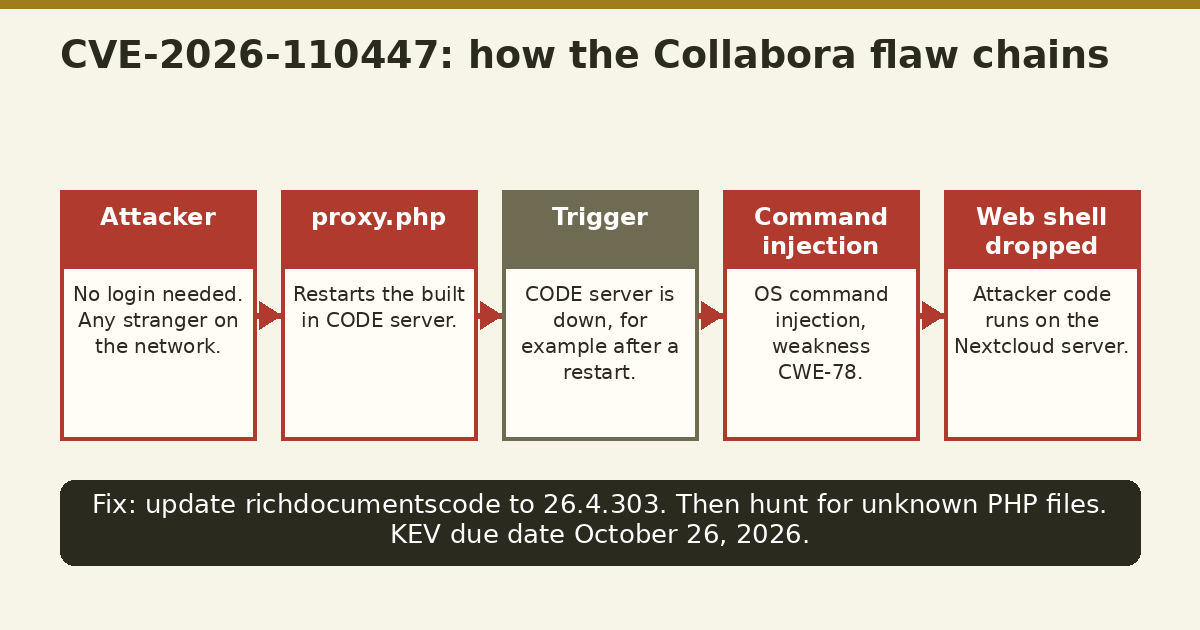
The Cybersecurity and Infrastructure Security Agency (CISA) added CVE-2026-110447 to its Known Exploited Vulnerabilities (KEV) catalog on October 23, 2026. Common Vulnerabilities and Exposures (CVE) is the public record system. The flaw is an OS command injection in the Collabora Online Built-in CODE Server, a Nextcloud app called richdocumentscode.
Why this flaw is an incident story, not just a patch story
The CVE record states exploitation in the wild in September and October 2026. Users found web shells on their servers. One reported shell was a one line PHP backdoor in the app folder.
That detail changes the work. A patch closes the flaw. A web shell is a foothold. If the shell ran before you patched, the attacker may have read data on that box. You cannot answer that question without a hunt.
The fix is richdocumentscode 26.4.303. The hunt is a file review plus access log review back to early September. Look for unknown PHP files and for proxy.php hits in the logs.
The DFARS clock
Defense Federal Acquisition Regulation Supplement (DFARS) clause 252.204-7012 requires rapid reporting of cyber incidents. If covered defense information sat on the affected server, a confirmed web shell is a cyber incident.
The reporting clock is 72 hours from discovery. Discovery means the moment you confirm compromise, not the moment you patched. The report goes to the DoD Cyber Incident portal. Keep the timeline tight: when the shell landed, what it touched, what you removed, what you patched.
Even without a confirmed shell, keep evidence of the negative result. The log review and the file hunt are proof of due diligence. An assessor or a contracting officer will ask what you checked.
PolicyCortex does not clean web shells or file incident reports. Your team does that work. PolicyCortex helps organize the evidence that follows.
What to do this week
Patch to 26.4.303. Hunt for web shells first, then decide whether the incident clock applies.
Sources
- CVE-2026-110447 record, CVE Program.
- CVE-2026-110447 detail, National Institute of Standards and Technology.
- CISA KEV catalog, added October 23, 2026, due October 26, 2026.
- Nextcloud community forum notice, "To Collabora Built-in User: Update ASAP," October 3, 2026.
- DFARS 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting.
- Original diagram by PolicyCortex.
Next step
Want incident and patch evidence kept in one place? See how PolicyCortex collects it from live systems.