Guides / October 22, 2026
GitLab RCE and DFARS Incident Reporting Duties
A code host compromise is a reporting problem, not only a patch problem. Defense contractors need both plans ready before an incident.
CVE-2026-110264 shows why that readiness matters. Its Common Vulnerability Scoring System (CVSS) score is 10.0, Critical. It is a remote code execution (RCE) flaw in GitLab.
What happened in GitLab
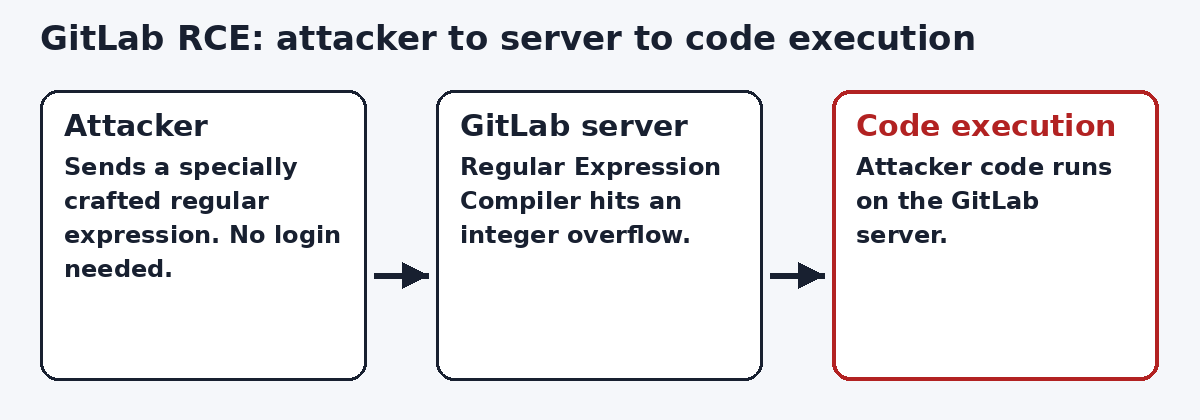
The Common Vulnerabilities and Exposures record describes an integer overflow. It occurs when a specially crafted regular expression is compiled.
Under certain conditions, an unauthenticated user could run arbitrary code. That code runs on the GitLab server itself.
GitLab Community Edition (CE) is in scope. GitLab Enterprise Edition (EE) is in scope too. Affected versions begin at 7.0, before 18.11.13. Every 19.x line is affected before its fixed release.
GitLab released the fixes on October 21, 2026. The fixed releases are 19.5.1 and 19.4.3. They also include 19.3.6, 19.2.9, and 19.1.9. The last two are 19.0.10 and 18.11.13.
The record credits researcher joaxcar with the report. GitLab received it through HackerOne.
The reporting clock under DFARS
The Defense Federal Acquisition Regulation Supplement (DFARS) sets contract duties. Clause 252.204-7012 covers safeguarding and cyber incident reporting.
A cyber incident on a covered system triggers rapid reporting. The clause uses a 72 hour reporting window. Teams must also preserve images and monitoring data.
A GitLab server can hold covered defense information. Source code and technical data often sit in repositories. If that server is hit, the clock question starts immediately.
This article does not say this flaw caused any incident. GitLab has reported patches, not a confirmed breach here. The lesson is to decide the reporting path in advance.
Decide the path before you need it
Write down who checks for compromise signs. Write down who contacts the contracting officer. Write down where logs and server images get preserved.
Patching first and planning later loses evidence. Preserve logs while the upgrade work proceeds. Keep both work streams in the incident record.
Actions for this week
Find each self managed GitLab install you operate. Compare its version with the affected ranges. Upgrade to the fixed release for its line. Then check logs for signs of odd server behavior.
Sources
- CVE-2026-110264 record, CVE Program. Updated October 22, 2026.
- GitLab patch release for 19.5.1, GitLab. https://docs.gitlab.com/releases/patches/patch-release-gitlab-19-5-1-released/
- DFARS clause 252.204-7012, safeguarding and reporting. https://www.acquisition.gov/dfars/252.204-7012-safeguarding-covered-defense-information-and-cyber-incident-reporting
- Original diagram by PolicyCortex.
More incident reporting readiness guides live at dfarsreadiness.com.