Guides / October 24, 2026
Identity Systems Are in Scope for DFARS Flaw Work
Defense contractors focus on the apps that hold data. They forget the systems that guard the door to those apps.
On October 22, 2026, Okta Trust published two security advisories for Okta Access Gateway (OAG). OAG is an appliance that puts Okta sign on in front of company apps. If your apps hold covered defense information, the gateway is part of your safeguarding story.
The two flaws
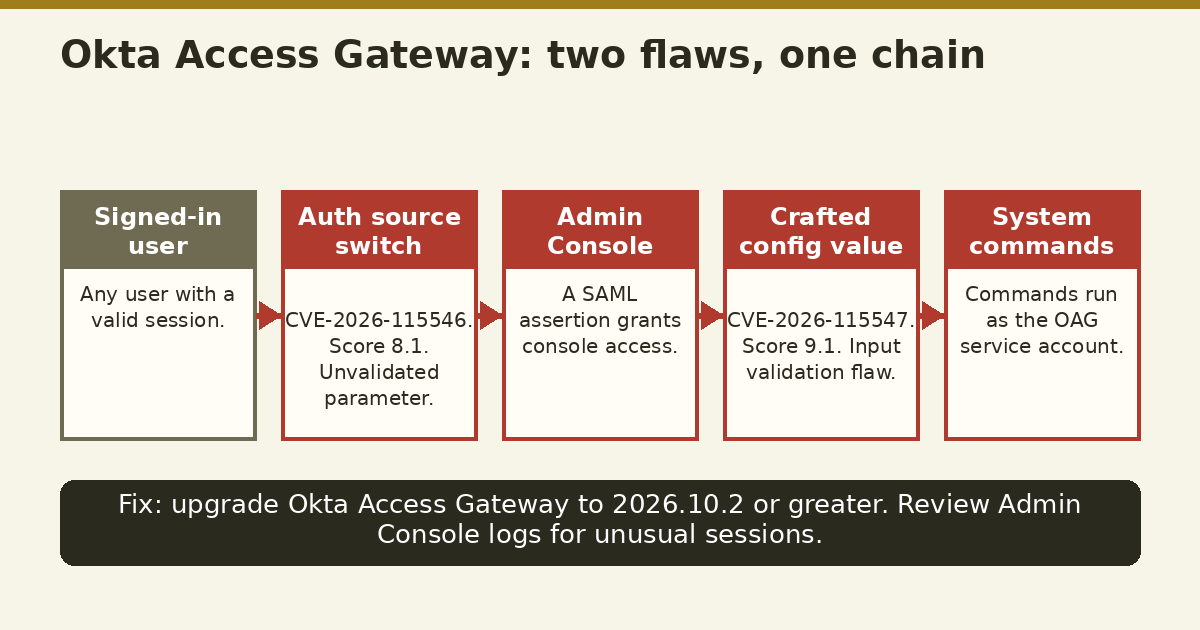
The first record is CVE-2026-115547. Common Vulnerabilities and Exposures (CVE) is the public record system. It is an input validation failure in the Admin Console. An authenticated administrator can run system commands as the OAG service account. The score is CVSS 3.1 9.1, critical.
The second record is CVE-2026-115546. A signed-in user can change the auth source parameter at sign on. The gateway then issues a SAML assertion for the Admin Console. Security Assertion Markup Language (SAML) is the login token standard. The score is CVSS 3.1 8.1, high.
Together they chain. A signed-in user becomes an admin. The admin becomes command execution on the appliance. Both are fixed in OAG 2026.10.2.
The DFARS angle
Defense Federal Acquisition Regulation Supplement (DFARS) clause 252.204-7012 requires adequate security on covered contractor information systems. An identity gateway that brokers access to those systems is in scope. Its flaws are your flaws.
No exploitation has been reported. Neither CVE is in the CISA KEV catalog as of October 23, 2026. That is good news, not a reason to wait. Patch now and the story stays a maintenance entry. Wait, and a future KEV listing turns it into an incident entry with a 72 hour reporting clock.
Your evidence file should hold three items. The current appliance version. The upgrade ticket to 2026.10.2 or greater. The Admin Console log review. If a contracting officer asks about identity safeguards, this is the file you open.
PolicyCortex does not patch Okta appliances. Your team applies vendor fixes. PolicyCortex helps organize the evidence that follows.
What to do this week
Upgrade OAG to 2026.10.2 or greater. File the version proof with your safeguarding evidence.
Sources
- Okta Trust security advisory, Command Execution via Admin Console Input in Okta Access Gateway, October 22, 2026.
- Okta Trust security advisory, Authentication Source Verification Issue in Okta Access Gateway, October 22, 2026.
- CVE-2026-115547 record, CVE Program.
- CVE-2026-115546 record, CVE Program.
- DFARS 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting.
- Original diagram by PolicyCortex.
Next step
Want safeguarding evidence kept in one place? See how PolicyCortex collects it from live systems.