Guides / October 22, 2026
Stolen Workstation Credentials Can Start a DFARS Incident Clock
Defense Federal Acquisition Regulation Supplement (DFARS) clause 252.204-7012 sets duties. Contractors must report cyber incidents rapidly to the government.
Rapid means within 72 hours of discovery. That clock makes early facts precious.
A command line interface (CLI) swap tested that readiness. OVHcloud publishes the CLI for cloud work.
Its advisory is GHSA-862f-55f5-vmvw. No Common Vulnerabilities and Exposures (CVE) number applies.
What was taken, per the advisory
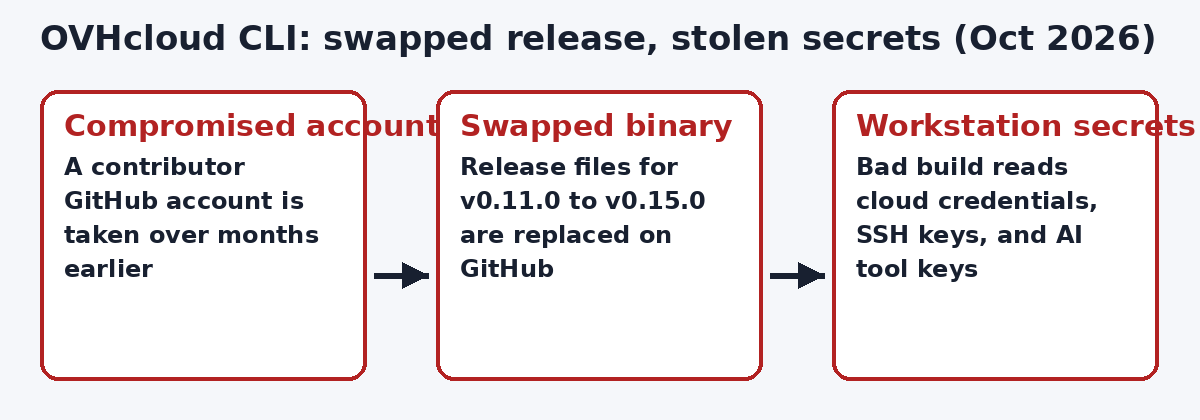
OVHcloud says a compromised developer account acted. It replaced binaries for v0.11.0 through v0.15.0.
Files were live from 12:47 to 14:21. That is Coordinated Universal Time on October 19, 2026.
OVHcloud reports about 250 downloads then. The build was made to steal disk secrets.
Its target list includes cloud credentials. It includes Secure Shell keys and Terraform credentials.
It also includes artificial intelligence tool keys. Those keys can open other services quickly.
The Hacker News reports the checksums.txt swap. On v0.15.0, the hash file was replaced too.
OVHcloud shipped v0.16.0 as the fix. It is immutable and has a signed tag.
The reportable incident path
Start with one affected contractor workstation. Its cloud credential gets copied by the build.
That credential guards systems holding covered information. Now the exposure is no longer theoretical.
Discovery starts your 72 hour clock. Your team must preserve images and logs.
Your team must also review access records. Stolen credentials invite follow on access attempts.
Whether a report is due depends on facts. Counsel and your contracting officer guide that call.
But the path itself should be planned. Waiting to design it wastes the clock.
Preparation that shortens the clock
Keep an inventory of admin workstation tools. Know which credentials each tool can reach.
Keep download and install logs with dates. The October 19 window decides exposure here.
Keep a rotation runbook for cloud keys. Practice it before an advisory forces it.
A checksum hosted beside the binary is not proof. Prefer signed, immutable release sources instead.
The governance lesson
You cannot govern tools you never inventoried. Unknown tools create unknown incident paths.
Map the path from workstation to covered systems. Write it down before you need it.
PolicyCortex does not distribute or clean CLI tools. This article covers incident readiness only.
What to do this week
Check for installs inside the October 19 window. Rotate secrets on any affected workstation.
Brief your incident lead on this path. Confirm the 72 hour reporting steps today.
Sources
- OVHcloud security advisory GHSA-862f-55f5-vmvw, ovh/ovhcloud-cli repository. Versions, window, downloads, targets, and fix.
- DFARS clause 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting. https://www.acquisition.gov/dfars/252.204-7012
- "Hackers Hijack Five OVHcloud CLI Releases," The Hacker News, October 2026. https://thehackernews.com/2026/10/hackers-hijack-five-ovhcloud-cli.html Checksums.txt swap detail.
- Original diagram by PolicyCortex.
Next step
Want incident evidence kept ready before the clock starts? See how PolicyCortex keeps it.