Guides / October 25, 2026
Pillow 13.0.0: Patch Evidence Your DFARS File Needs Now
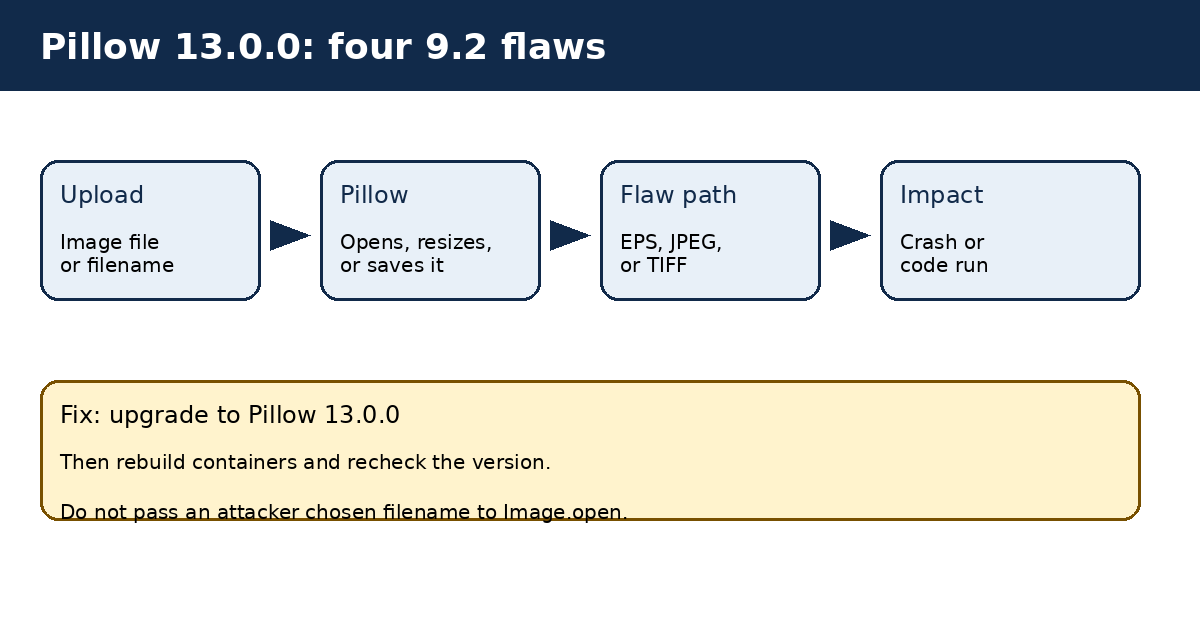
Defense Federal Acquisition Regulation Supplement (DFARS) clause 252.204-7012 requires safeguarding of covered defense information. That duty covers the libraries that touch that information. Pillow is one of them in many systems.
Pillow is a Python imaging library. It opens, converts, resizes, and saves images. Pillow 13.0.0 arrived October 16, 2026. It fixes four flaws scored 9.2.
The four flaws
Common Vulnerabilities and Exposures (CVE) is the public record system. The Common Vulnerability Scoring System (CVSS) rates severity from 0 to 10.
- CVE-2026-112900: EPS filename injection into Ghostscript.
- CVE-2026-112398: FlashPix JPEG heap overflow on a normal open.
- CVE-2026-112403: Lossless JPEG heap overflow on draft or thumbnail.
- CVE-2026-112393: TIFF save heap overflow to memory.
A flaw in an image library can become a flaw in a document system. Document systems often hold the very information DFARS protects. Treat the patch as safeguarding work, not housekeeping.
What the DFARS file should hold
List every system that handles covered defense information and uses Pillow. Record the version in each system. Include containers and bundled copies.
Record the upgrade date per system. Pillow 13.0.0 is the fixed version. Test first, because it drops Python 3.10. Rebuild container images. Recheck the version after deploy. Keep the recheck result with the file.
Also note flowdown. If a subcontractor system uses Pillow, the same record applies there. A prime cannot show safeguarding with a gap at a supplier.
No wild exploitation is reported in the advisories checked. None of the four IDs is in the CISA Known Exploited Vulnerabilities catalog as checked October 25, 2026. Patch while that is still true.
Sources
- Pillow 13.0.0 release notes, October 16, 2026.
- CVE-2026-112900 record, CVE Program.
- CVE-2026-112398 record, CVE Program.
- CVE-2026-112403 record, CVE Program.
- CVE-2026-112393 record, CVE Program.
- Original diagram by PolicyCortex.
Next step
Want safeguarding evidence linked to each system? See how PolicyCortex collects it from live systems.