Guides / October 21, 2026
If Plex2Shell Hit Your Network, DFARS 252.204-7012 Starts a 72 Hour Clock
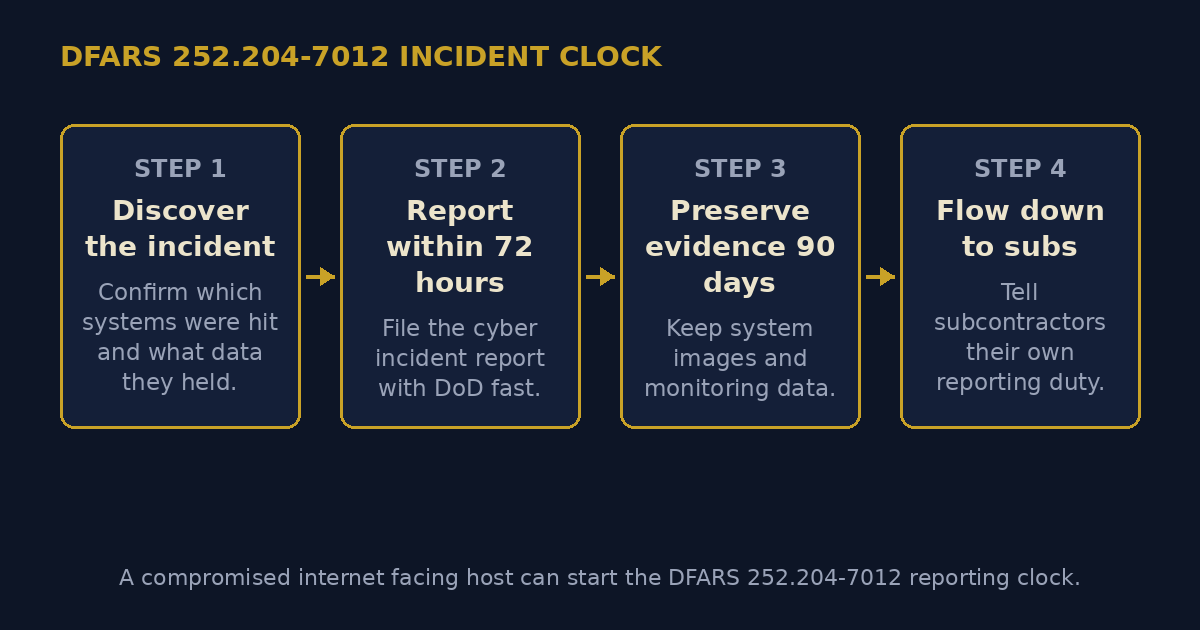
A media server on your office network can start a federal reporting clock. That is the DFARS lesson in Plex2Shell.
On October 20, 2026, CISA added four Plex Media Server flaws to its Known Exploited Vulnerabilities catalog. The flaws are CVE-2026-96652, CVE-2026-96654, CVE-2026-96655, and CVE-2026-96656. (CISA alert) Attackers chain them into code execution with no login. Plex says servers older than build 1.43.3.10861 that faced the internet should be treated as possibly compromised.
If that server sat on a network that holds covered defense information, you may owe the Department of Defense a report.
What the clause asks for
DFARS is the Defense Federal Acquisition Regulation Supplement. Clause 252.204-7012 covers safeguarding and incident reporting for covered defense information. (DFARS 252.204-7012)
A cyber incident that affects covered defense information must be reported to the Department of Defense rapidly. The common working target is 72 hours from discovery. Waiting to be sure is not the standard. Discovery starts the clock.
What counts as discovery here
Discovery is when you learn a system may be compromised. Plex's own guidance says to assume compromise for older internet facing servers. That statement can start your clock.
You do not need proof that covered defense information left the building. The clause covers incidents that affect it. A compromised host on the same network as that data is enough to investigate and report.
What to gather in the first hours
First, confirm the facts. Which systems ran Plex Media Server below build 1.43.3.10861? Which ones faced the internet? Write down versions and dates.
Second, preserve evidence. The clause requires keeping images of affected systems and monitoring data for at least 90 days. Image the hosts before you rebuild them.
Third, check what the host could reach. List shared folders, credentials, and any covered defense information on the same network segment.
Fourth, file the report through the DoD portal at dibnet.dod.mil. You need a DoD approved medium assurance certificate in advance. If you do not have one, get the process started now.
Flow it down
The clause flows to subcontractors when their work involves covered defense information. A subcontractor hit by Plex2Shell must report to DoD and give the report number to the next tier up.
Ask your subcontractors this week whether they run internet facing Plex or similar media servers. You do not want to learn about their incident from DoD.
Sources
- CISA Adds Six Known Exploited Vulnerabilities to Catalog, CISA, October 20, 2026. https://www.cisa.gov/news-events/alerts/2026/10/20/cisa-adds-six-known-exploited-vulnerabilities-catalog
- DFARS 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting. https://www.acquisition.gov/dfars/252.204-7012-safeguarding-covered-defense-information-and-cyber-incident-reporting
- Original diagram by PolicyCortex.
Next step
Want your incident evidence collected from the live system instead of assembled by hand? See how PolicyCortex builds it on Azure.