Guides / October 22, 2026
A Backdoored WordPress Site Can Trigger DFARS 252.204-7012
DFARS is the Defense Federal Acquisition Regulation Supplement. Clause 252.204-7012 covers safeguarding and incident reporting for covered defense information. (DFARS 252.204-7012)
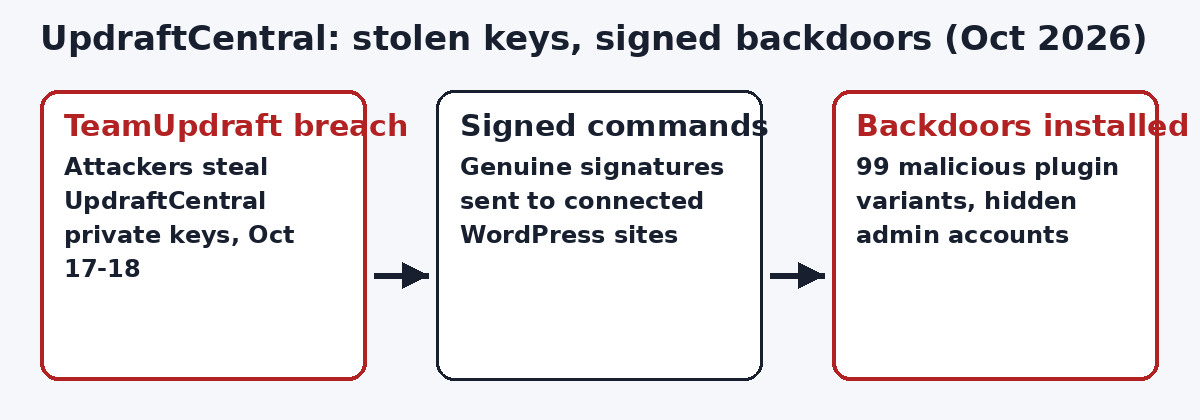
Over the weekend of October 17 and 18, 2026, attackers broke into TeamUpdraft's website. They stole the private keys behind UpdraftCentral, the remote management service for UpdraftPlus. They used those keys to push backdoor plugins to connected WordPress sites as properly signed commands.
Security firm Nethemba found the campaign on its own servers. Security firm Patchstack counted 99 malicious plugin names installed between 15:32 UTC on October 18 and 09:23 UTC on October 19.
When the clause applies
The clause requires a rapid report when a cyber incident occurs on a covered contractor information system or involves covered defense information. The report goes to the Department of Defense Cyber Crime Center (DC3) through DIBNet within 72 hours of discovery.
Many contractors run public WordPress sites. If that site is a covered contractor information system, or if the backdoor reached one, the incident is reportable. Malicious software on the system is the trigger. You do not need proof that data was taken.
The scope problem
The backdoor creates a hidden admin account and a login cookie that skips the login form. Removing the plugin does not remove the account. The attacker had full site control for the sites that were hit.
For the report, the affected system list must include every site that held a live UpdraftCentral key during the campaign window. That inventory is the first thing the clause expects you to have.
The key dates
TeamUpdraft's update history matters for your report. Version 1.26.12 was meant to revoke the old keys but did not delete them. Versions 1.26.13 and 2.26.13 remove keys created before 12:07 UTC on October 18.
Keys created between 12:07 and 21:00 UTC that day survive the update and must be deleted by hand. Your report should record which of your keys fell in that window and when you removed them.
What to do this week
Check every WordPress site in your scope for unknown plugins and accounts. Update, rotate keys, and delete the manual window keys by hand.
If any covered system was hit, start the 72 hour clock at discovery and file the DIBNet report. The clause rewards fast reporting, not complete forensics.
Sources
- Security incident disclosure, TeamUpdraft, October 19, 2026. Vendor's primary incident statement.
- "Stolen UpdraftCentral Keys Are Backdooring WordPress Sites," Patchstack, October 19, 2026. https://patchstack.com/articles/updraftcentral-key-compromise-wordpress-backdoors/
- Campaign analysis, Nethemba, October 19, 2026. First detailed researcher analysis of the campaign.
- DFARS 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting. https://www.acquisition.gov/dfars/252.204-7012-safeguarding-covered-defense-information-and-cyber-incident-reporting
- Original diagram by PolicyCortex.
Next step
Want incident evidence assembled from the live system instead of from memory? See how PolicyCortex collects it on Azure.