Guides / October 22, 2026
An Exploited Gateway Flaw Starts the DFARS 7012 Clock
Defense Federal Acquisition Regulation Supplement (DFARS) clause 252.204-7012 is about incidents. It is not about patches alone.
The Cybersecurity and Infrastructure Security Agency (CISA) listed two flaws on October 13, 2026. One flaw sits in a gateway many contractors run. That listing should start an internal review today.
The gateway flaw
The record is CVE-2026-104935. Common Vulnerabilities and Exposures (CVE) is the record system.
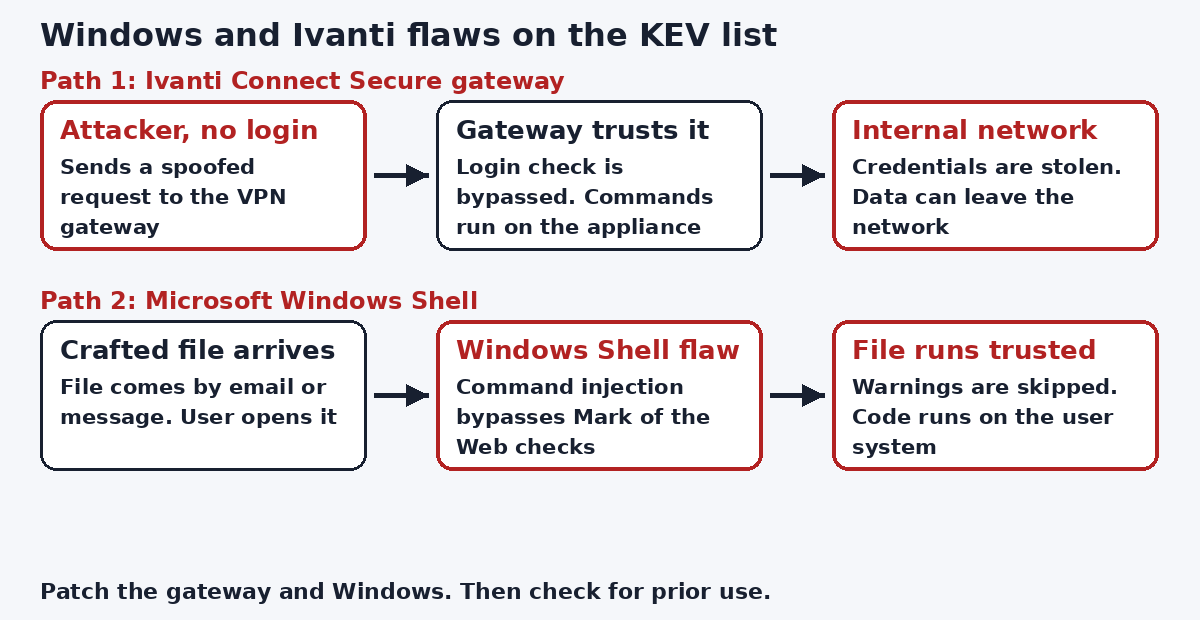
Ivanti Connect Secure is a Virtual Private Network (VPN) gateway. The flaw lets an attacker bypass login by spoofing. The attacker can then run commands remotely.
CISA says attackers used it for credential theft. CISA also says attackers used it for data theft. CISA added it to Known Exploited Vulnerabilities (KEV).
Affected builds include 22.8R2.4 and prior builds. Affected builds also include two 25.1 build lines. Ivanti disclosed the flaw on October 13, 2026.
The Windows flaw listed beside it
The second record is CVE-2026-96951. It is a Windows Shell command injection flaw. It can bypass Mark of the Web checks.
A crafted file can skip safety warnings. That matters on systems that handle contract files. Both flaws had an October 16 federal due date.
When the 72 hour clock starts
Clause 7012 requires a rapid incident report. The report is due within 72 hours of discovery. Discovery means you discover a cyber incident.
A KEV listing alone is not an incident. Evidence of use on your gateway is different. Log review and forensics decide that question.
Do not wait for perfect proof before reporting. The clause expects a report while facts develop. Your team can update the report later.
The 90 day evidence duty
Clause 7012 also requires evidence preservation. You must preserve images and relevant files. The preservation period is 90 days minimum.
That duty covers the affected gateway itself. It also covers logs and monitoring records. Do not reset the appliance before preserving evidence.
CISA advises a factory reset for suspected compromise. That advice follows preservation, not before it. CISA also warns the vendor checker may miss use. Attacker commands can run in memory only.
Preserve network logs from outside the appliance too. Those logs may hold what memory activity hid.
PolicyCortex does not patch Windows or Ivanti products. Vendors ship those fixes. PolicyCortex helps teams keep incident evidence organized.
What to do this week
Check if you run an affected gateway build. Review gateway logs back to October 1, 2026. Preserve relevant records before any reset work.
Sources
- CVE-2026-104935 record, CVE Program. Updated October 13, 2026.
- CVE-2026-96951 record, CVE Program. Updated October 21, 2026.
- CISA Urges Patching Newly Exploited Vulnerability in Ivanti Connect Secure, CISA, October 13, 2026. https://www.cisa.gov/news-events/alerts/2026/10/13/cisa-urges-patching-newly-exploited-vulnerability-ivanti-connect-secure
- DFARS clause 252.204-7012, Safeguarding Covered Defense Information and Cyber Incident Reporting.
- Original diagram by PolicyCortex.
Next step
Want incident evidence kept in one dated record? See how PolicyCortex organizes it from live systems.